Compliance is the IT job Europe keeps creating: AI Act, NIS2, DORA
European IT postings kept falling after the new rules arrived. The rules still changed the jobs: compliance, governance and named regulations moved into leadership and security ads, and the security chief moved closer to the CEO.
Part of the AI-era IT jobs series. Start with CIO and IT manager jobs grew 26 %. The managers under them got cut..
In the winter of 2022-23, not one of the 148 security job pages I collected from company career sites named NIS2, DORA, the EU AI Act, the Cyber Resilience Act or ISO 42001. In May to October 2026, 14.2 % of the Europe-based security ads named at least one of them, against 3.9 % of the US ones [job-page study, 2026]. Over the same period, IT operations postings in Germany and France kept falling. The laws have not reversed that fall. They have written new duties into the IT and security jobs that remain, created governance and risk work in regulated sectors, and moved the security chief closer to the CEO.
Five dates in twelve months
The EU AI Act came into force on 1 August 2024. NIS2 had to be in national law by 17 October 2024, and on 28 November 2024 the Commission wrote to 23 member states that had missed the deadline [European Commission, 2024]. NIS2 covers 18 sectors. DORA has applied to 20 types of financial entity since 17 January 2025 [EIOPA, 2026]. The AI Act's bans and its duty to train staff in AI literacy applied from 2 February 2025, and the rules for general-purpose models from 2 August 2025. The high-risk obligations were due on 2 August 2026 until the Digital Omnibus, published in July 2026, moved them to 2 December 2027 for stand-alone systems and to 2 August 2028 for AI built into regulated products [Gibson Dunn, 2026].
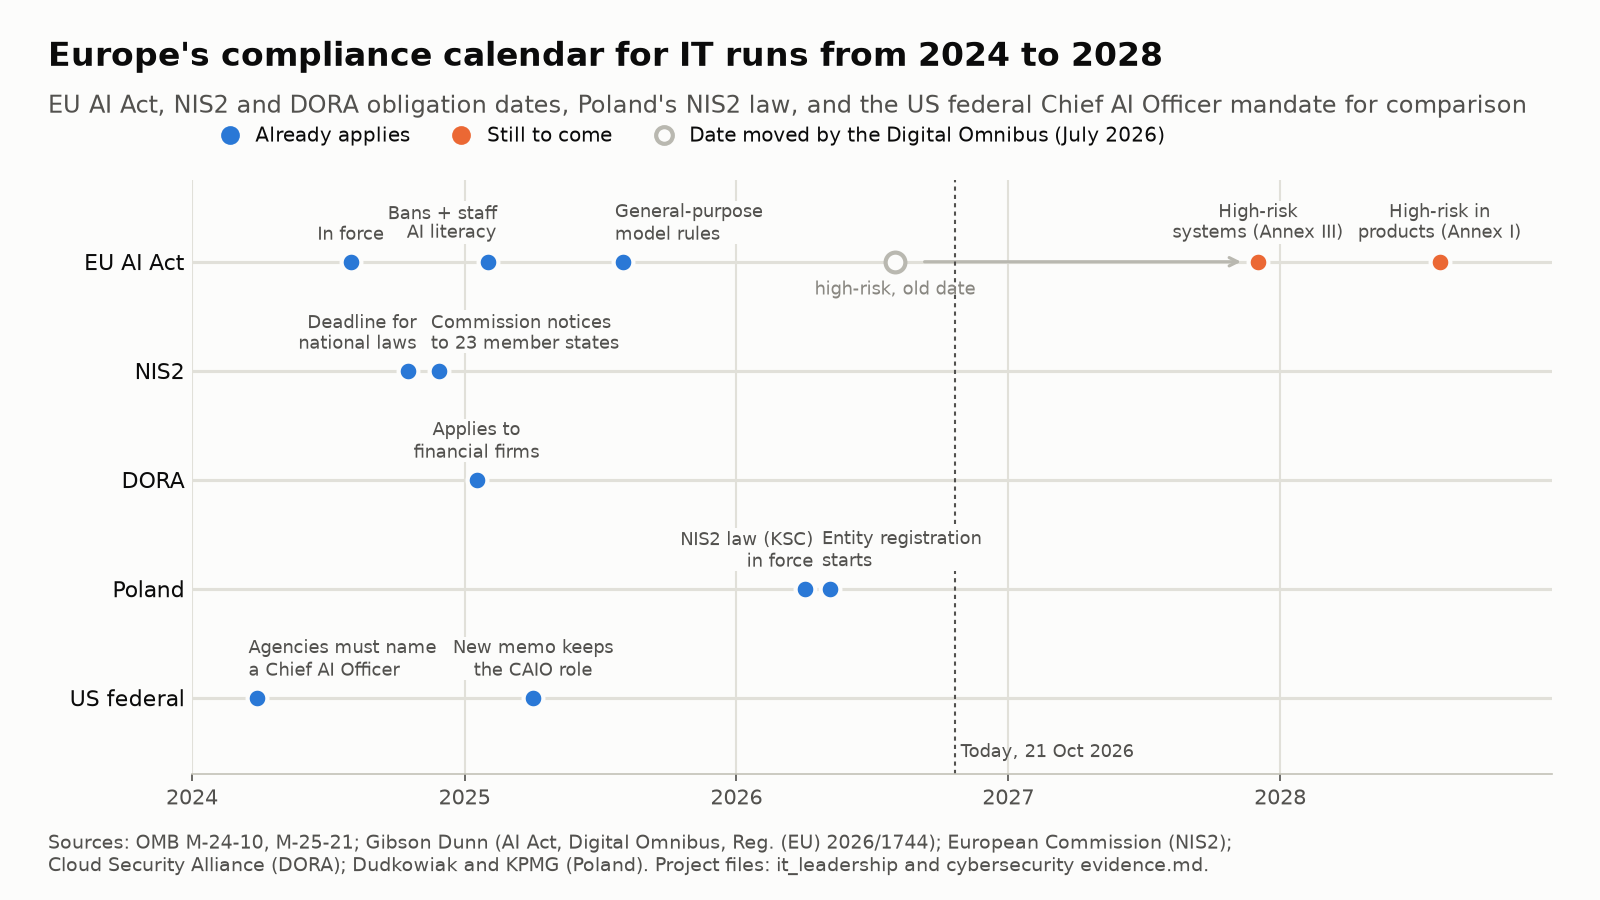
The closest US step in this window was inside government. A federal memo of March 2024 gave every agency 60 days to name a Chief AI Officer, and the April 2025 memo that replaced it kept the role [OMB, 2024 and 2025].
The deadlines show up in budgets. In ENISA's 2025 survey of 1,080 organisations, 70 % named NIS2 and compliance as the main driver of their security spending, and 76 % struggled to attract IT specialists [HaystackID, 2025].
Compliance moved into the job ad
I counted compliance terms in two sets of company job pages. The first is IT leadership ads, 57 from October 2022 to March 2023 and 116 from May to October 2026. The second is security ads, 148 and 914 for the same periods. The counting script removes legal boilerplate such as "in compliance with applicable laws", and it ignores "DORA" where an engineering ad means the DevOps delivery metrics of that name.
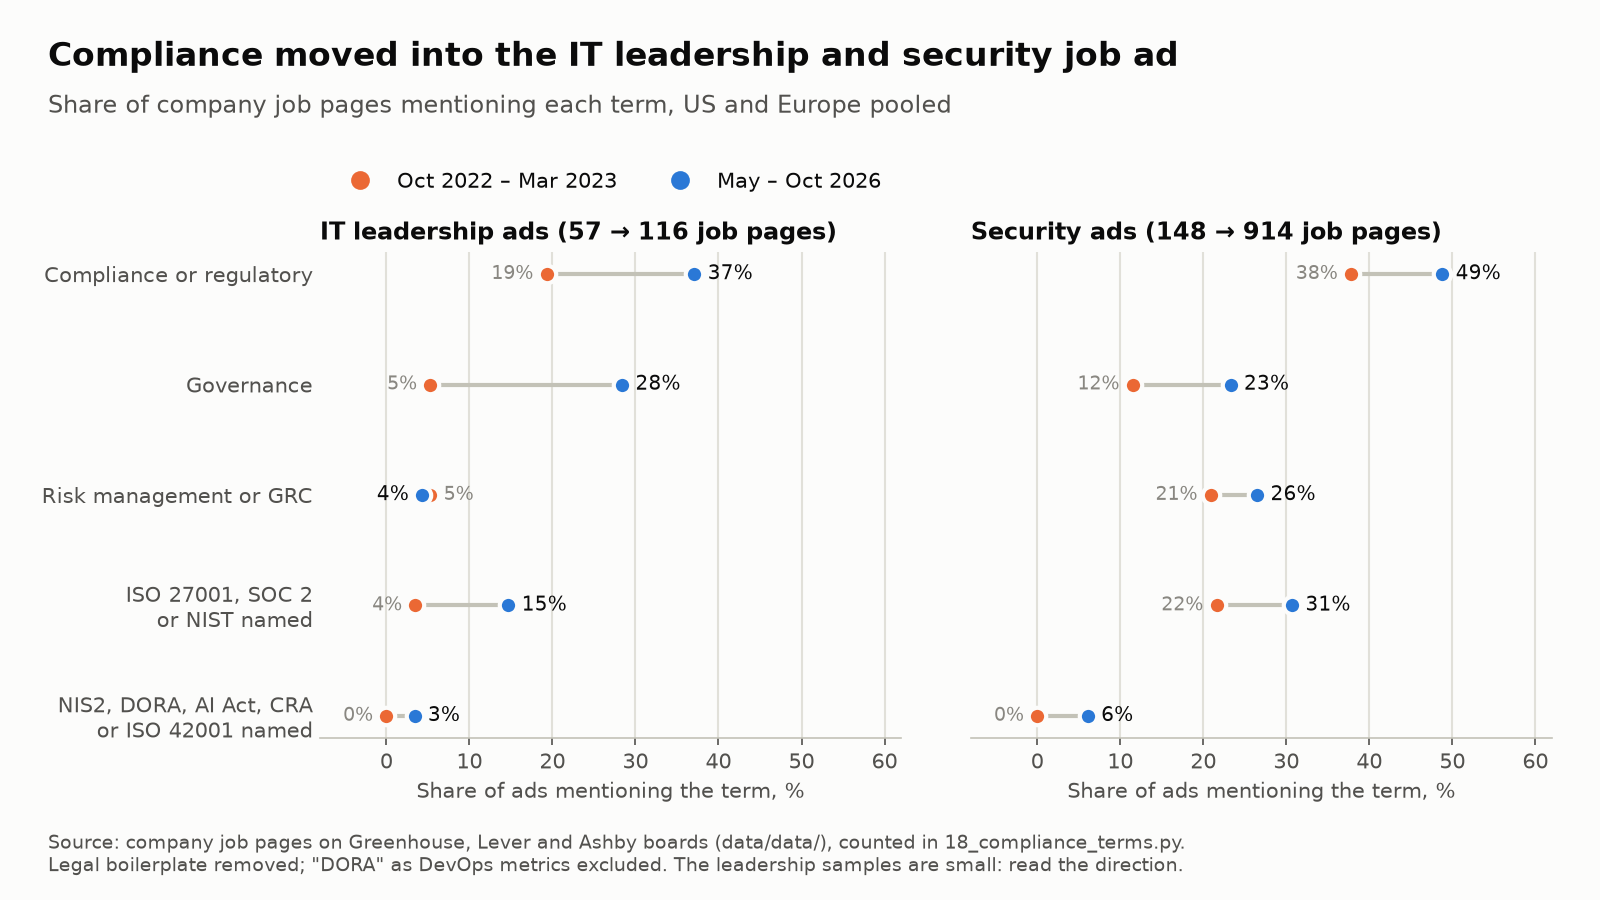
In leadership ads, "compliance" or "regulatory" went from 19 % to 37 %. "Governance" went from 5 % to 28 %, and ads that name ISO 27001, SOC 2 or NIST went from 4 % to 15 %. In security ads the base was already higher. Compliance went from 38 % to 49 %, named security standards from 22 % to 31 % and governance from 12 % to 23 % [job-page study, 2026].
The European split is where the regulation shows. In security ads, 14.2 % of the 120 Europe-based pages named NIS2, DORA, the AI Act, the Cyber Resilience Act or ISO 42001, against 3.9 % of 436 US pages. Among leadership ads, 13 of the 22 Europe-based pages in 2026 mention compliance, against 1 of 11 in 2022-23. Those leadership samples are small, so read them as direction. The ads are specific. An N26 controls manager designs controls for ISO 27001, GDPR, DORA, NIS2 and the AI Act. Adyen's security programme manager oversees DORA and other Dutch central bank mandates. GetYourGuide's GRC manager will "shape how we meet obligations like NIS2" [job-page study, 2026].
AI governance became part of the security job at the same time. In ISACA's 2025 survey, 47 % of security professionals had helped develop AI governance in their organisation, up from 35 % a year earlier [ISACA, 2025].
Fewer openings, more duties
None of this turned into more openings. Indeed's index of IT operations and helpdesk postings in Germany averaged 100 in August 2024, the month the AI Act came into force, and 65 in September 2026. France went from 119 to 63. The US index fell less, from 77 to 70 [Indeed via FRED, 2026].
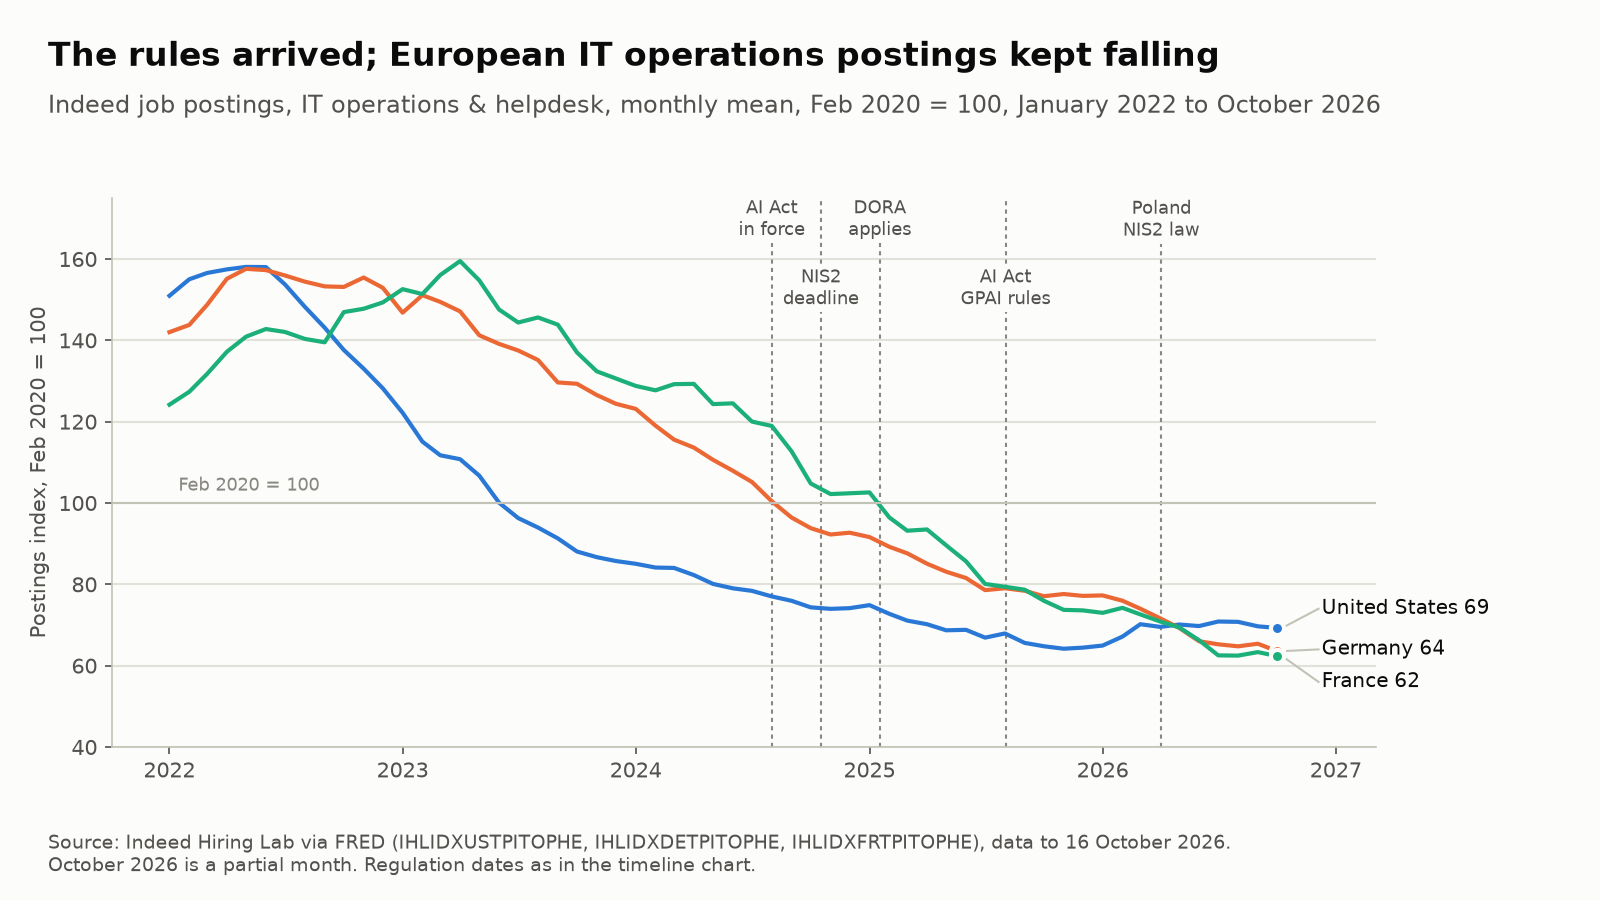
Nothing in this data says the rules caused that fall. The synthesis report behind this series reads Europe's continued decline after 2024, while US postings recovered, as the closest thing to an AI effect in the postings data [synthesis report, 2026]. The rules did not offset it either. The EU's vacancy rate in information and communication fell from 3.9 % to 2.2 % between late 2022 and late 2025, while the number of ICT specialists in work grew from 9.37 million to 10.45 million [Eurostat, 2026]. My reading is that employers are keeping the people they have and adding the new duties to existing jobs.
The duties also changed who reports to whom. Heidrick & Struggles found 5 % of CISOs reporting to the CEO in 2023, 14 % in 2024 and 42 % in 2025 [Heidrick & Struggles, 2024 and 2025]. NIS2 and DORA make management answer for cyber and ICT risk, and boards responded by moving their security chief closer. A recruiter's 2026 guide to the German market calls DORA the single biggest source of GRC work in financial services [Barclay Simpson, 2026]. The AI side shows up in titles more than in compliance. UK adverts for a "Head of AI" went from 20 in 2024 to 151 in 2026 [ITJobsWatch, 2026], and 38.5 % of Fortune 1000 firms had a Chief AI Officer by early 2026 [DataIQ, 2026].
From the vendor side, this looks like GDPR again. Most GDPR work arrived after its deadline, and I expect the same here. The synthesis report behind this series forecasts that European GRC and AI-governance hiring peaks in 2027-28, with medium confidence [synthesis report, 2026].
Poland: late, then all at once
Poland transposed NIS2 about eighteen months late. The amended national cybersecurity act (KSC) came into force on 3 April 2026, and essential and important entities have been registering since 7 May 2026 [Dudkowiak and KPMG, 2026]. In June 2026 the Sejm also passed Poland's own act on AI systems, which sets up a national supervisory commission, KRiBSI [DWF, 2026].
The demand was there before the law. On LinkedIn, Poland had the second-highest concentration of cyber job demand of 14 countries, 3.5 % of all postings, in 2024 [LinkedIn Economic Graph, 2024]. Cyber ads on No Fluff Jobs roughly doubled between the first quarter and the autumn of 2025 [Antyweb, 2025]. Polish firms are late on AI itself: 8.4 % of firms with ten or more staff used AI in 2025, against 20.0 % across the EU [Eurostat, 2026]. For Polish IT teams the regulatory work in 2026 is mostly NIS2. AI Act work comes later, and the synthesis report puts Poland's GRC hiring peak in 2028 [synthesis report, 2026].
What this means if you work in IT in Europe
- Learn to map one regulation to controls and evidence: NIS2 for most sectors, DORA in finance, the AI Act if your company builds or deploys AI. Security ads that name ISO 27001, SOC 2 or NIST went from 22 % to 31 %, and the European ones now name the EU rules on top.
- If you are starting out, look at governance, risk and compliance work in a regulated sector. A bank under DORA or an essential entity under NIS2 still needs people to collect evidence and own controls, and someone has to answer for them.
- If you run IT, budget for compliance headcount in 2027 whatever happens to your AI plans. Most of the work lands after the deadlines, and the AI Act's high-risk duties start in December 2027.
NIS2 and DORA evidence starts with knowing what you run and how it is connected, which is the configuration record Sensaka's CMDB & ITSM module keeps.
Sources
- Mustard Seed Solutions, job-page study: compliance, governance, risk and regulation terms in IT leadership ads (ai-era-it-jobs study data, 57 vs 116 company job pages) and security ads (ai-era-it-jobs study data compared sample, 148 vs 914), October 2022 to March 2023 vs May to October 2026, Greenhouse, Lever and Ashby boards via Common Crawl, the Wayback Machine and live boards. Counts: ai-era-it-jobs study data, audit lines in the ai-era-it-jobs study data. Earlier count of the same security sample: ai-era-it-jobs study data.
- European Commission, "Commission calls on 23 Member States to fully transpose the NIS2 Directive", 28 November 2024. https://digital-strategy.ec.europa.eu/en/news/commission-calls-23-member-states-fully-transpose-nis2-directive ; NIS2 Directive policy page (18 sectors), updated 2 July 2026. https://digital-strategy.ec.europa.eu/en/policies/nis2-directive
- EIOPA, "Digital Operational Resilience Act (DORA)". https://www.eiopa.europa.eu/digital-operational-resilience-act-dora_en ; Cloud Security Alliance, "An Update on European Compliance: NIS2, CRA, DORA", 2025. https://cloudsecurityalliance.org/articles/an-update-on-european-compliance-nis2-cra-dora
- Gibson Dunn, "EU AI Act Omnibus Agreement: Postponed High-Risk Deadlines and Other Key Changes", 27 May 2026 (Regulation (EU) 2026/1744 published 24 July 2026). https://www.gibsondunn.com/eu-ai-act-omnibus-agreement-postponed-high-risk-deadlines-and-other-key-changes/
- US Office of Management and Budget, Memorandum M-24-10, 28 March 2024. https://www.whitehouse.gov/wp-content/uploads/2024/03/M-24-10-Advancing-Governance-Innovation-and-Risk-Management-for-Agency-Use-of-Artificial-Intelligence.pdf ; Memorandum M-25-21, 3 April 2025. https://www.whitehouse.gov/wp-content/uploads/2025/02/M-25-21-Accelerating-Federal-Use-of-AI-through-Innovation-Governance-and-Public-Trust.pdf
- HaystackID, summary of the ENISA NIS Investments Report 2025 (1,080 organisations), December 2025. https://newsline.haystackid.com/enisa-2025-nis-investments-report-technology-prioritized-as-cyber-talent-pools-contract/
- ISACA, State of Cybersecurity 2025, press release, 29 September 2025. https://www.isaca.org/about-us/newsroom/press-releases/2025/state-of-cybersecurity-2025-global-press-release
- Indeed Hiring Lab, IT operations & helpdesk job postings index, Germany, France and the US (IHLIDXDETPITOPHE, IHLIDXFRTPITOPHE, IHLIDXUSTPITOPHE), via FRED, data to 16 October 2026. https://fred.stlouisfed.org/series/IHLIDXDETPITOPHE ; https://fred.stlouisfed.org/series/IHLIDXFRTPITOPHE ; https://fred.stlouisfed.org/series/IHLIDXUSTPITOPHE (monthly means in the ai-era-it-jobs study data)
- Eurostat, job vacancy statistics, information and communication (jvs_q_nace2), Q4 2022 and Q4 2025. https://ec.europa.eu/eurostat/databrowser/view/jvs_q_nace2/ ; ICT specialists in employment (isoc_sks_itspt), 2022 and 2025. https://ec.europa.eu/eurostat/databrowser/view/isoc_sks_itspt/ ; enterprises using AI (isoc_eb_ai), 2025, updated 15 June 2026. https://ec.europa.eu/eurostat/databrowser/view/isoc_eb_ai/
- Heidrick & Struggles, "2024 Global CISO Organization and Compensation Survey". https://www.heidrick.com/en/insights/cybersecurity/2024-global-chief-information-security-officer-organization-and-compensation-survey ; "2025 Global CISO Compensation Survey". https://www.heidrick.com/en/insights/cybersecurity/2025-global-chief-information-security-officer-compensation-survey
- Barclay Simpson, "2026 Salary Survey & Recruitment Trends Guide: Cyber Security and Data Privacy in Germany" (recruiter view). https://www.barclaysimpson.com/?p=82635
- ITJobsWatch, UK permanent vacancy trends, "Head of AI", six months to 20 October 2024 and 2026, retrieved 20 October 2026. https://www.itjobswatch.co.uk/jobs/uk/head%20of%20ai.do
- Randy Bean / DataIQ, AI and Data Leadership Executive Benchmark Survey, 2026 edition summary. https://babl.ai/survey-finds-corporate-ai-adoption-moves-from-experimentation-to-deployment-at-scale/
- Dudkowiak, "NIS2 Directive in Poland"; KPMG Poland legal alert on the NIS2 implementation (KSC amendment of 23 January 2026, in force 3 April 2026). https://www.dudkowiak.com/regulatory-in-poland/nis-2-in-poland/ ; https://kpmg.com/pl/en/insights/law/legal-alert-the-nis2-directive-implemented-in-poland-new-cybersecurity-obligations-for-entrepreneurs.html
- DWF Poland, "Polska ustawa o systemach sztucznej inteligencji coraz bliżej", May 2026, and Sejm print 2614. https://dwfgroup.com/pl-pl/news-and-insights/insights/2026/5/polska-ustawa-o-systemach-sztucznej-inteligencji-coraz-blizej ; https://api.sejm.gov.pl/sejm/term10/prints/2614/2614.pdf
- LinkedIn Economic Graph, "Global Demand for Cybersecurity Talent Continues to Cool", July 2024. https://economicgraph.linkedin.com/content/dam/me/economicgraph/en-us/PDF/global-cybersecurity-talent-trends.pdf
- Antyweb, "Oferty pracy cyberbezpieczeństwo 2025" (No Fluff Jobs data), 2025. https://antyweb.pl/oferty-pracy-cyberbezpieczenstwo-2025
- Mustard Seed Solutions, "How AI changed the IT job market, 2022 → 2026, and where it goes 2027–2029", ai-era-it-jobs report, 21 October 2026, Section 13 forecasts. ai-era-it-jobs study data.
See hardware, power and cooling health from outside the operating system. Request an online trial and explore how Sensaka brings hardware, operations and business services into one platform.
Request an Online Trial →Sensaka AI & GPU Infrastructure Observability
Full-stack thermal, liquid cooling, and BMC hardware monitoring for high-density NVIDIA H100/B200 GPU racks and AI clusters.
Related articles & analysis